Roles and permissions control what users can do in your workspace. Rocket.Chat uses a role-based system where each role represents a defined set of permissions, and administrators assign roles to users to grant the appropriate level of access.
Role: A named set of permissions assigned to a user or group of users. Roles determine which features and controls a user can access. By default, roles appear as tags next to usernames on messages. To turn this on or off workspace-wide, go to Accounts → Default User Preferences → Hide Roles. Individual users can override this for their own account from Accessibility & appearance settings.
Permission: A specific feature or setting that can be granted to a role. Different roles have different default permissions, which you can review and modify on the Permissions screen.
To view roles and permissions in your workspace, go to Manage → Workspace → Permissions. The screen shows a table where:
Each row is a permission (the Name column lists permission names).
Each column is a role.
Each checkbox indicates whether the role in that column has the permission in that row.
Select or clear checkboxes to grant or revoke permissions for a role.
Scope of Rocket.Chat roles
Roles in Rocket.Chat have either a Global or Room scope.
Global scope
Global roles apply across the entire workspace, for example, admin. They can hold permissions that operate at the server level rather than within a specific room. For example, Create a Team is a global permission that lets a user create teams from anywhere in the workspace.
Room scope
Room-scoped roles control access to room-specific permissions. For example, you can grant the Edit Room permission to the Moderator role and any user set as a moderator in a specific room can edit that room's information. Visit Room Roles to learn more about the available room roles.
You can assign these roles to a user in an individual room or globally across the workspace.
In a room: Assign the role from the room's members list. Its permissions apply only to that room. See Room Roles for more details.
On the user account: Add the role to the Roles field when creating or editing a user in Manage → Workspace → Users. Its permissions apply across all rooms, including those where the user has no room-specific role. Visit Invite and Add Users for more details.
Categories of Rocket.Chat roles
Rocket.Chat provides three built-in categories of roles:
Administrator role
Workspace user roles
Omnichannel roles
Let’s look at the roles for each category.
Administrator role
A Rocket.Chat administrator has the admin role with Global scope, granting full access to the entire workspace. Admins can manage both workspace administration and omnichannel settings. The first user who registers and logs into a new workspace is automatically assigned the admin role.
Workspace user roles
Users can have one or more of the following roles, which together determine what actions they can perform.
Role | Scope | Description |
|---|---|---|
| Global |
|
| Global |
|
| Global |
|
| Global |
|
| Room | Moderators can manage messages, delete messages, and ban users from a specific channel. See Moderation for details on how to use this feature. |
| Room | You can assign your preferred set of permissions to the room leader for managing the room. |
| Room |
|
| Global | It allows a user to view and audit all messages within the workspace. Users with only the |
| Global | The |
| Global |
|
The
anonymousrole is removed in Rocket.Chat 9.0.0. Users who still have theanonymousrole when you update are deactivated and logged out. When Allow anonymous read is enabled in the Accounts settings, people can still read messages in public channels without signing in.
Omnichannel roles
Omnichannel roles let users interact with or manage Omnichannel features.
Role | Scope | Description |
|---|---|---|
| Global | Handles inquiries and support requests through Omnichannel. |
| Global | Manages agents and all other Omnichannel features. |
| Global | Views and monitors Livechat interactions and analytics. |
The administrator role, user roles, and Omnichannel roles are available by default in every Rocket.Chat workspace. To create roles tailored to your needs, see Custom Roles.
Edit roles

To edit a role:
Go to Manage → Workspace → Permissions.
Click the pencil icon next to the role name in the column header. The Role Editing panel opens.
Update the available fields, then click Save.
The following fields are shown in the Role Editing panel:
Field | Editable for default roles | Editable for custom roles | Description |
|---|---|---|---|
Role | No | No | The role's internal identifier (for example, |
Description | Yes | Yes | The label shown to users (for example, |
Scope | No | Yes | Determines whether the role applies workspace-wide (Global) or only inside specific rooms (Rooms). Editable only for custom roles. |
Users must use Two Factor Authentication | Yes | Yes | When enabled, users with this role must use 2FA for certain workspace actions, such as logging in or changing settings. Make sure 2FA is configured in your workspace. |
Custom roles can also be deleted from this panel. Default roles cannot be deleted.
View and assign users to roles
To see which users are assigned to a role, click Users in role at the bottom of the Role Editing panel. From this view you can also add users to the role or remove them.
The following screenshot shows an example of the user role:
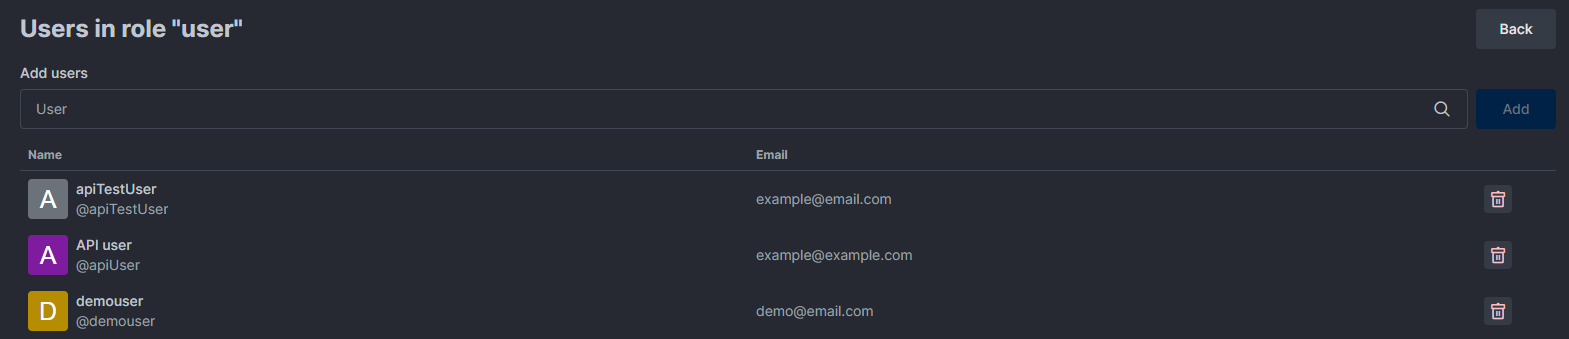
For room-scope roles, you must first select a room. The list then shows users who hold that role in the selected room. Users who hold the role on their account, rather than in that room, are not listed. The user must already be a member of the room before you can assign them a room-scope role.
The following screenshot shows the Moderator role in a room called random:
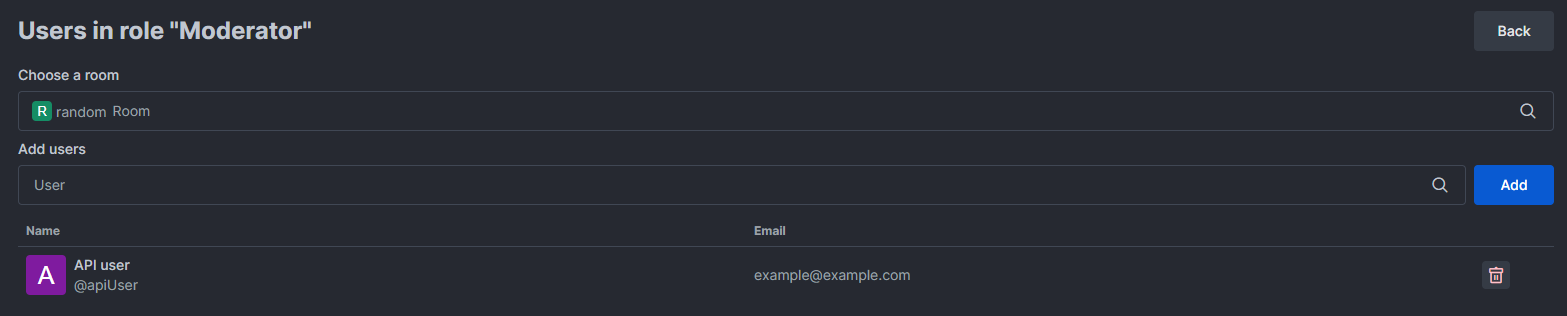
In this example, search for the user and click Add to give other users the Moderator role in the random room. The user must belong to the selected room before you can assign a role to them.
For information on creating custom roles, see Custom Roles.
For information on permissions and settings, see Permissions.
Roles and permissions can also be managed via the REST API. See Roles API and Permissions API for details.